
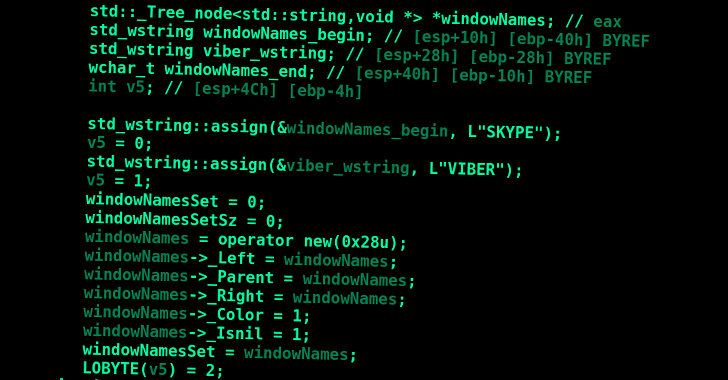
New Discovery of Hacker Group Linked to Cyberattacks Targeting Companies in Conflict Zones of Russia and Ukraine Reveals Group May Be Longer Than Previously Thought became.
Tracked as a threat actor bad magic (aka Red Stinger) has been associated not only with new and sophisticated campaigns, but also with activity clusters first revealed in May 2016.
In a technical report released by Russian cybersecurity firm Kaspersky, “Previous targets were primarily in the Donetsk, Luhansk and Crimean regions, but now they have expanded in scope, targeting individuals, diplomats and other individuals in western and central Ukraine. Institutions, research institutes,” he said. last week.
The campaign will feature a new modular framework codenamed CloudWizard. The framework has features such as taking screenshots, recording microphones, recording keystrokes, retrieving passwords, and collecting Gmail inboxes.
Bad Magic was first documented by the company in March 2023, when the group used a backdoor called PowerMagic (aka DBoxShell or GraphShell) and a modular framework called CommonMagic in attacks targeting the Russian-occupied territories of Ukraine. is detailed.
And earlier this month, Malwarebytes revealed at least five waves of espionage attacks carried out by this group dating back to December 2020.
Deeper insights shared by Kaspersky linked Bad Magic to previous activity based on scrutiny of historical telemetry data, allowing the company to identify various artifacts associated with the CloudWizard framework.
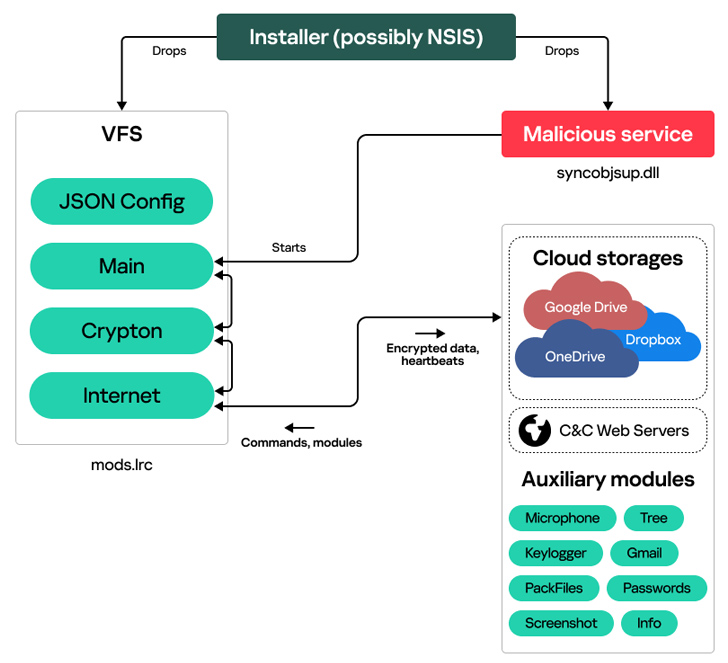
The initial access vector used to drop the first stage installer is currently unknown. However, the malware is configured to drop a Windows service (“syncobjsup.dll”) and a second file (“mods.lrc”), which contain sensitive data to collect and extract. It contains three different modules for
The information is sent in encrypted form to an attacker-controlled cloud storage endpoint (OneDrive, Dropbox, or Google Drive). The web server is used as a fallback mechanism in case none of the services are reachable.
Kaspersky has announced that it has identified source code duplication between an older version of CloudWizard and another malware known as Prikormka discovered by Slovak cybersecurity firm ESET in 2016.
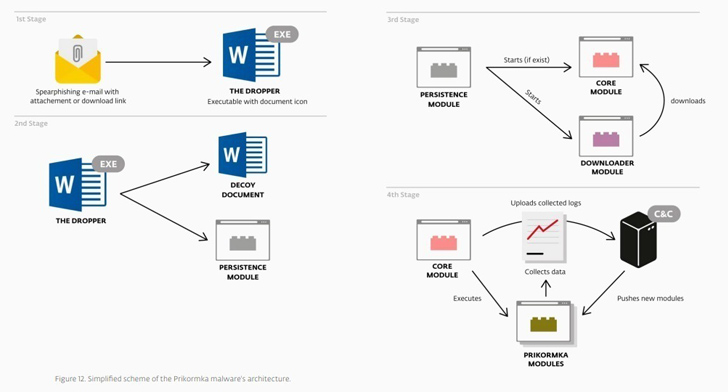 |
| Image Source: ESET |
The espionage campaign, monitored by ESET under the name of Operation Groundbait, primarily targeted separatists in Donetsk and Luhansk, as well as Ukrainian officials, politicians and journalists.
Deployed via droppers in malicious email attachments, Prikormka has 13 different components to collect different types of data from compromised machines. ESET-collected evidence indicates that this malware has been in selective use since at least 2008.
Zero Trust + Deception: Learn How to Outsmart Attackers!
See how Deception can detect advanced threats, stop lateral movement, and strengthen your Zero Trust strategy. Join us for an insightful webinar!
Reserve your seat!
CloudWizard also shows similarities to a related intrusion set called BugDrop published by CyberX (which was then acquired by Microsoft) in 2017, and the industrial cybersecurity firm claims CloudWizard is more advanced than Groundbait. explains.
Commonalities such as victimology and source code duplication have also been found between CloudWizard and CommonMagic, indicating that the threat actor has been iteratively tweaking its malware arsenal and infecting its targets for nearly 15 years. is shown.
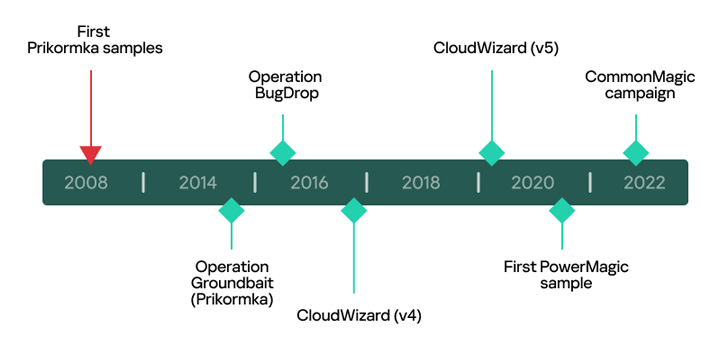
The latest developments attribute the CloudWizard framework to the attackers behind Operation Groundbait and Operation BugDrop, hoping to finally reveal the full picture of the mysterious group’s origins. One more piece is provided to the puzzle to solve.
“For more than 15 years, the attackers behind these operations have continually enhanced their toolset, targeted organizations of interest, and relentlessly pursued cyber espionage,” said Kaspersky researcher George Kucherin. We have shown continuous efforts,” he said.
“Geopolitical factors remain an important motivation for APT attacks, and given the prevailing tensions in the disputed regions of Russia and Ukraine, the attackers are expected to continue their operations for the foreseeable future. increase.”